Safely turn suspect files into actionable intelligence, without putting the mission at risk.
Helheim gives cyber operators an isolated environment for malware triage at the mission edge. Analyze unknown files in minutes using static analysis, dynamic detonation, and safe sample handling, without relying on a remote lab.
Average cost of a ransomware breach in 2025
Average recovery time after ransomware impact
Average cost of a ransomware breach in 2025
Average recovery time after ransomware impact
PROVEN CAPABILITIES
Three capabilities work together to examine a file, observe its behavior, and preserve the sample safely.
Hash lookups, antivirus signature checks, and metadata extraction characterize a sample at first contact.
An isolated detonation sandbox runs suspicious files so operators can observe how malware behaves.
Encryption, fragmentation, and header modification keep stored samples inert while preserving them for analysis.
A machine-learning pipeline extracts behavioral features from sandbox telemetry and flags samples as malicious or benign.
ARCHITECTURE
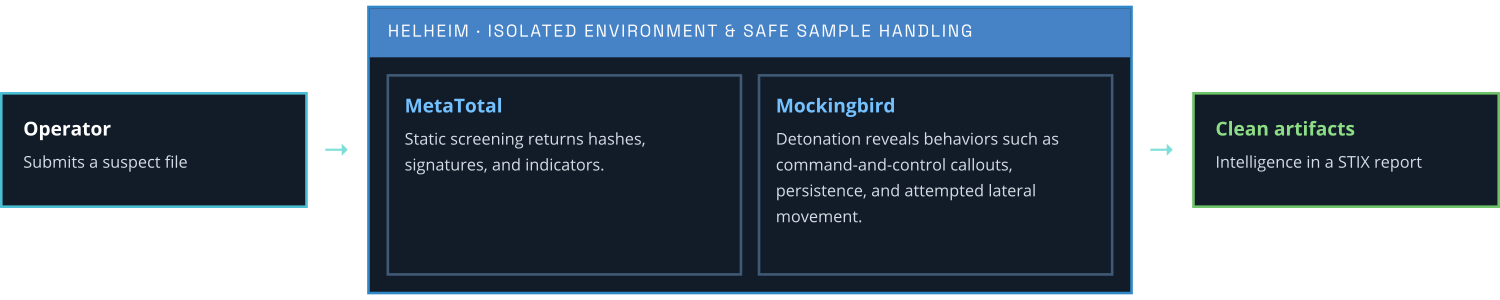
The suspect file enters a controlled environment. Only non-executable artifacts leave it.
MISSION-READY
01
DISCOVERY
Suspect file identified
An alert, a user report, or an unusual process leads an operator to a file they cannot identify or attribute.
02
STATIC
Screen the file against antivirus engines
The operator submits the file to Helheim. MetaTotal screens it against widely used antivirus engines and returns hashes, signatures, and indicators in minutes.
03
DYNAMIC
Detonate the sample in isolation
If the file is unknown, suspicious, or warrants deeper analysis, the operator runs it in Mockingbird to observe its behavior.
04
ACT
Act on mission intelligence
Using the non-executable artifacts Helheim returns, the operator can update defenses, hunt for related indicators, and inform mission decisions.
WHY HELHEIM
Mockingbird is designed to elicit behavior from evasive malware that might otherwise recognize a sandbox.
MISSION VALUE
Faster malware triage at the mission edge
Lower risk of accidental infection
A repeatable workflow that reduces operator error
Intelligence to inform decisions in real time
AI-assisted verdicts that shorten time to a decision
Support across skill levels, operational tempos, and environments

Analyze malware without putting the mission at risk.
Discover how Helheim can support your cybersecurity objectives. Complete the contact form below to connect with our team and explore how Helheim can meet your mission needs.
Subscribe to our newsletter